Secret Manager
The initial minimal deployment stores the key used to encrypt secrets in / Forensic Acquisition and Investigation locally on the machine. Enabling a Secret Manager allows / Forensic Acquisition and Investigation to instead store the key in Azure Key Vault.
Prerequisites
- Ability to create a Key Vault
- Ability to update Role Assignments
Steps
- In the resource group click Create and search for “Key Vault” and select “Key Vault”
- Add a Key vault name
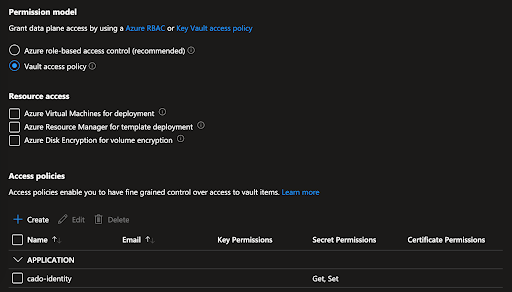
- Set Access Configuration to “Vault access policy”
- On “Access policies” search for “cado-identity” and select. Confirm the Client ID is the correct one.
- Go to the created resource. Copy the “Vault URI”
- Enable in the UI: Settings > Advanced > Secret Management
- Enter the “Vault URI” from step 5 and click Turn On Secrets Manager